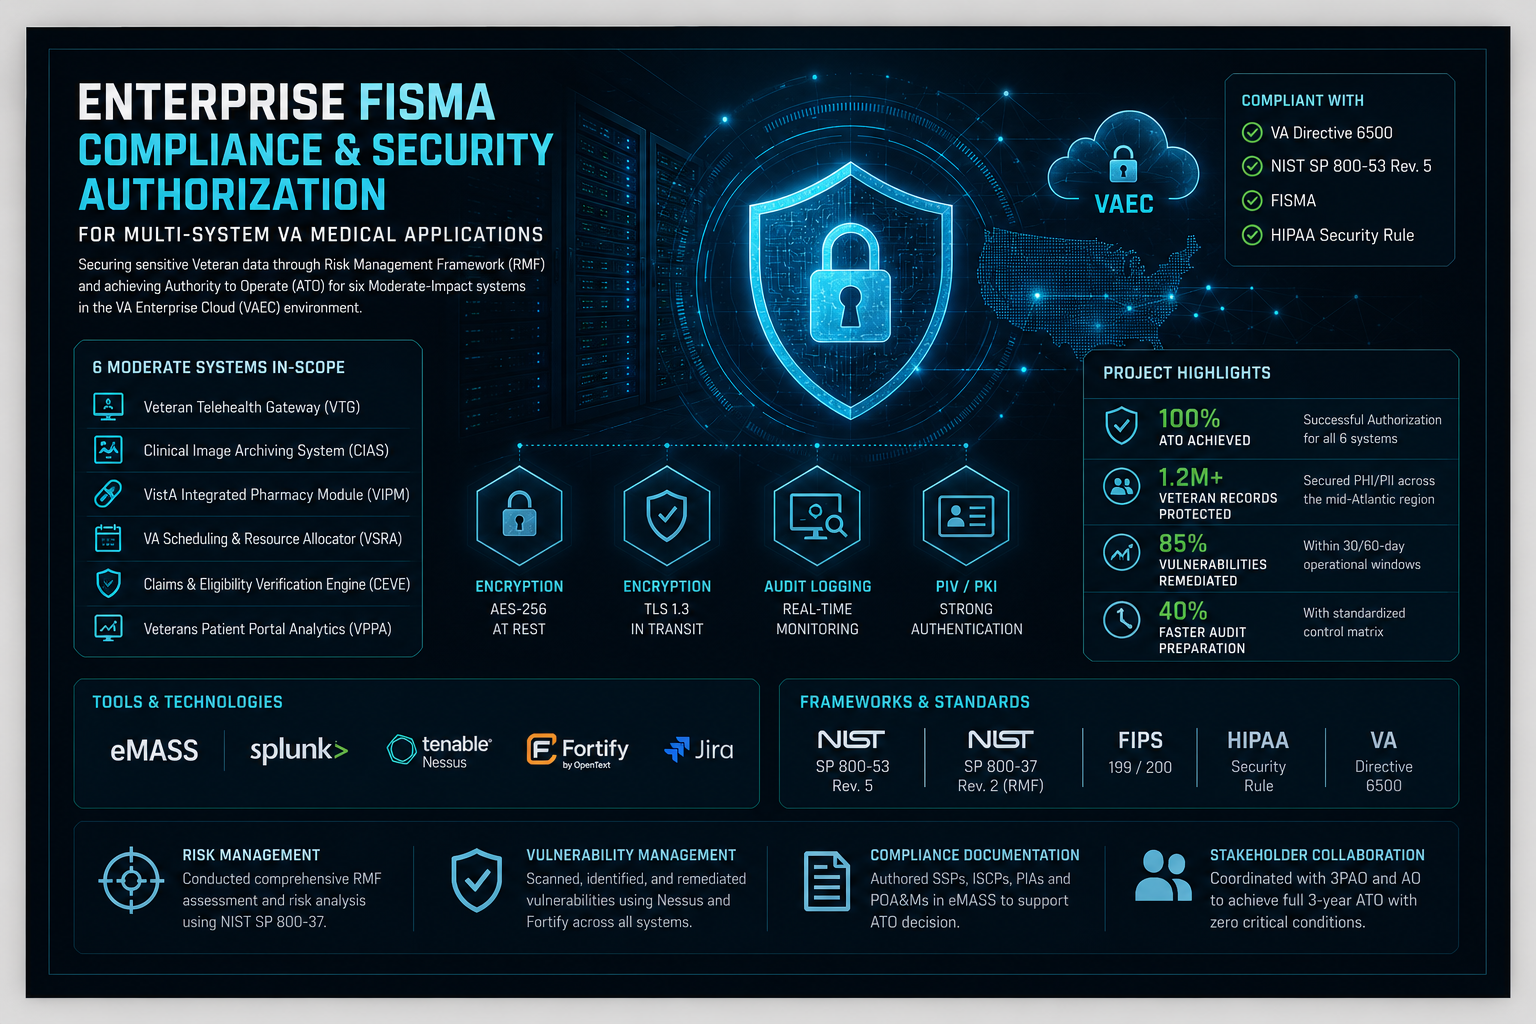
Enterprise FISMA Compliance & Security Authorization Led the Risk Management Framework (RMF) assessment and security authorization for six Moderate-Impact VA medical applications. The project focused on protecting sensitive Veteran PHI and PII while ensuring compliance with FISMA, HIPAA, and NIST SP 800-53 Rev. 5 standards. Successfully supported the systems through assessment and Authority to Operate […]
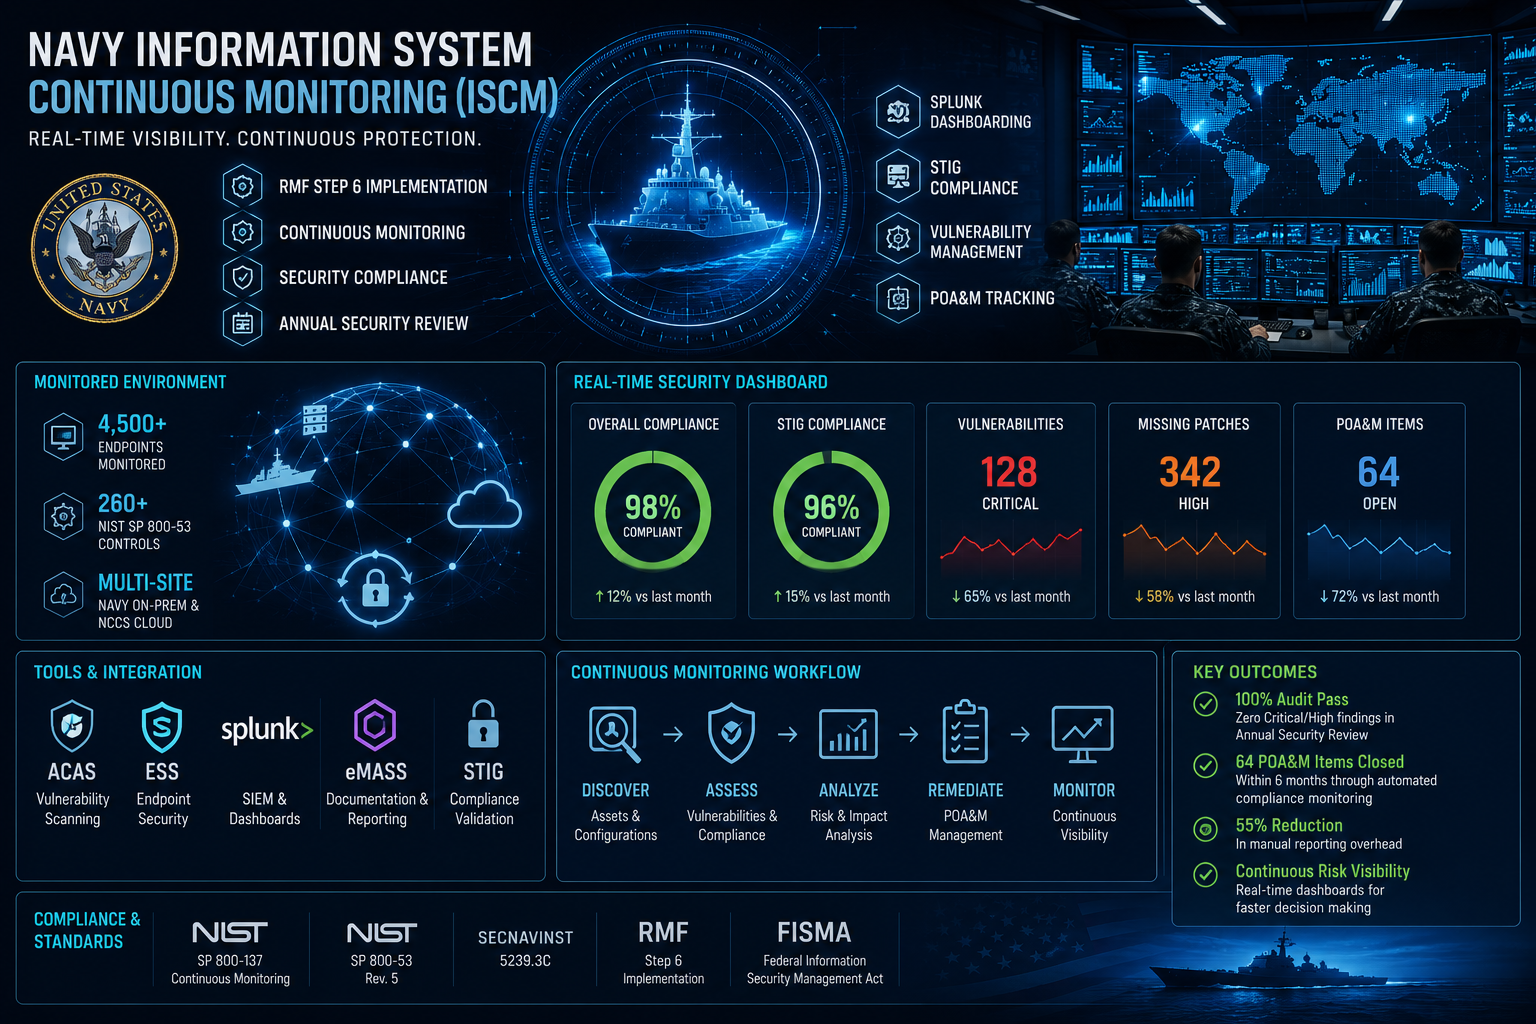
Navy Information System Continuous Monitoring (ISCM)
Navy Information System Continuous Monitoring (ISCM) Designed and implemented a comprehensive Information System Continuous Monitoring (ISCM) strategy for a mission-critical U.S. Navy environment. The project enhanced real-time security visibility, automated compliance monitoring, and ensured successful Annual Security Review (ASR) readiness while aligning with NIST SP 800-137 and RMF Step 6 requirements. RMF Step 6 Implementation […]
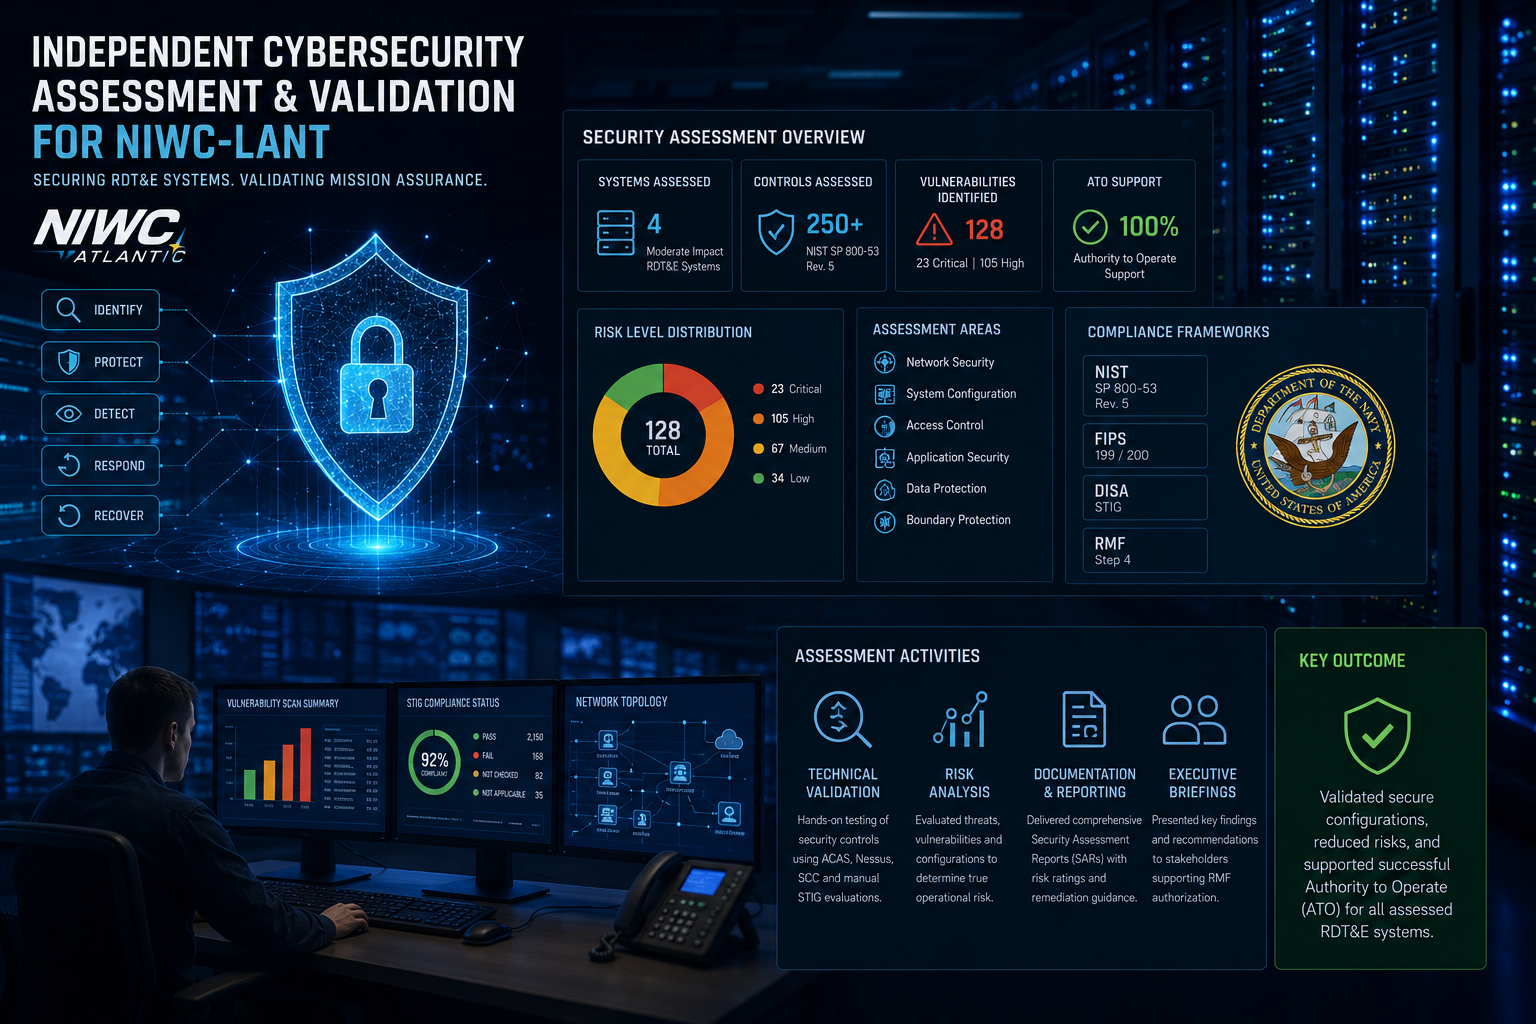
Independent Cybersecurity Assessment & Validation for NIWC-LANT
Independent Cybersecurity Assessment & Validation for NIWC-LANT Served as a Navy Qualified Validator (NQV) conducting independent cybersecurity assessments for four Moderate-Impact Research, Development, Test, and Evaluation (RDT&E) systems. The project focused on validating NIST SP 800-53 security controls, performing technical security assessments, and supporting successful Authority to Operate (ATO) approvals. Security Control Assessment RMF Step […]
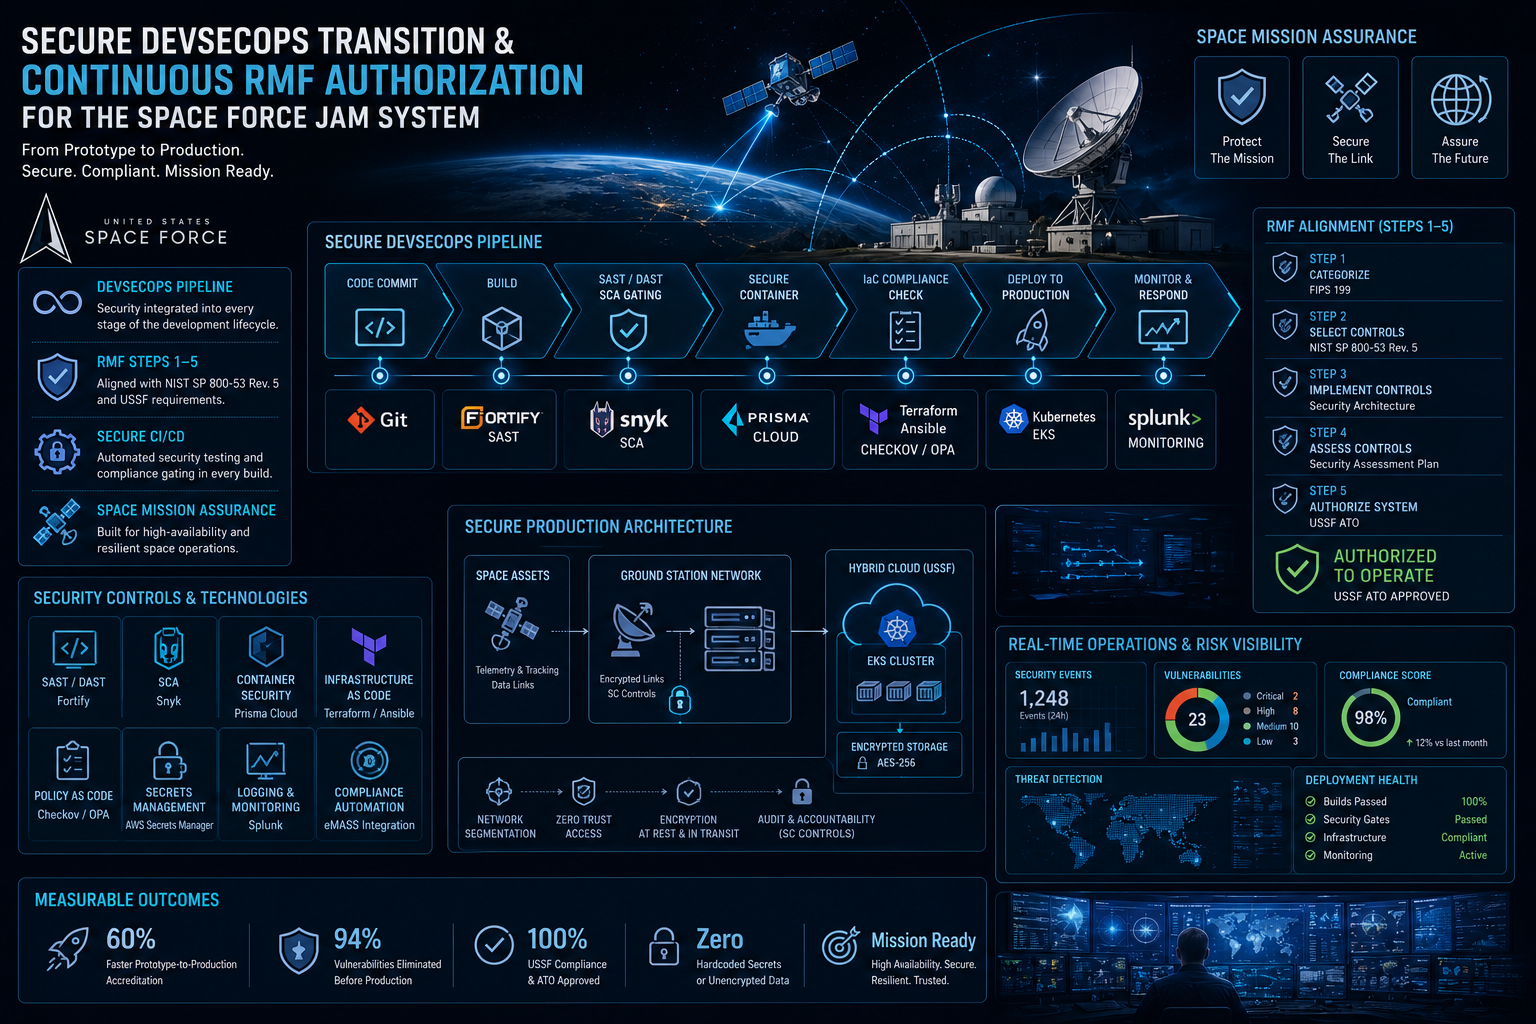
Secure DevSecOps Transition & Continuous RMF Authorization
Secure DevSecOps Transition & Continuous RMF Authorization Designed and implemented a secure DevSecOps architecture for the Space Force Joint Antenna Management (JAM) system, enabling its transition from prototype to production. Integrated automated security testing, continuous RMF compliance, and cloud security controls to support a secure Authority to Operate (ATO). DevSecOps Pipeline RMF Steps 1–5 Secure […]