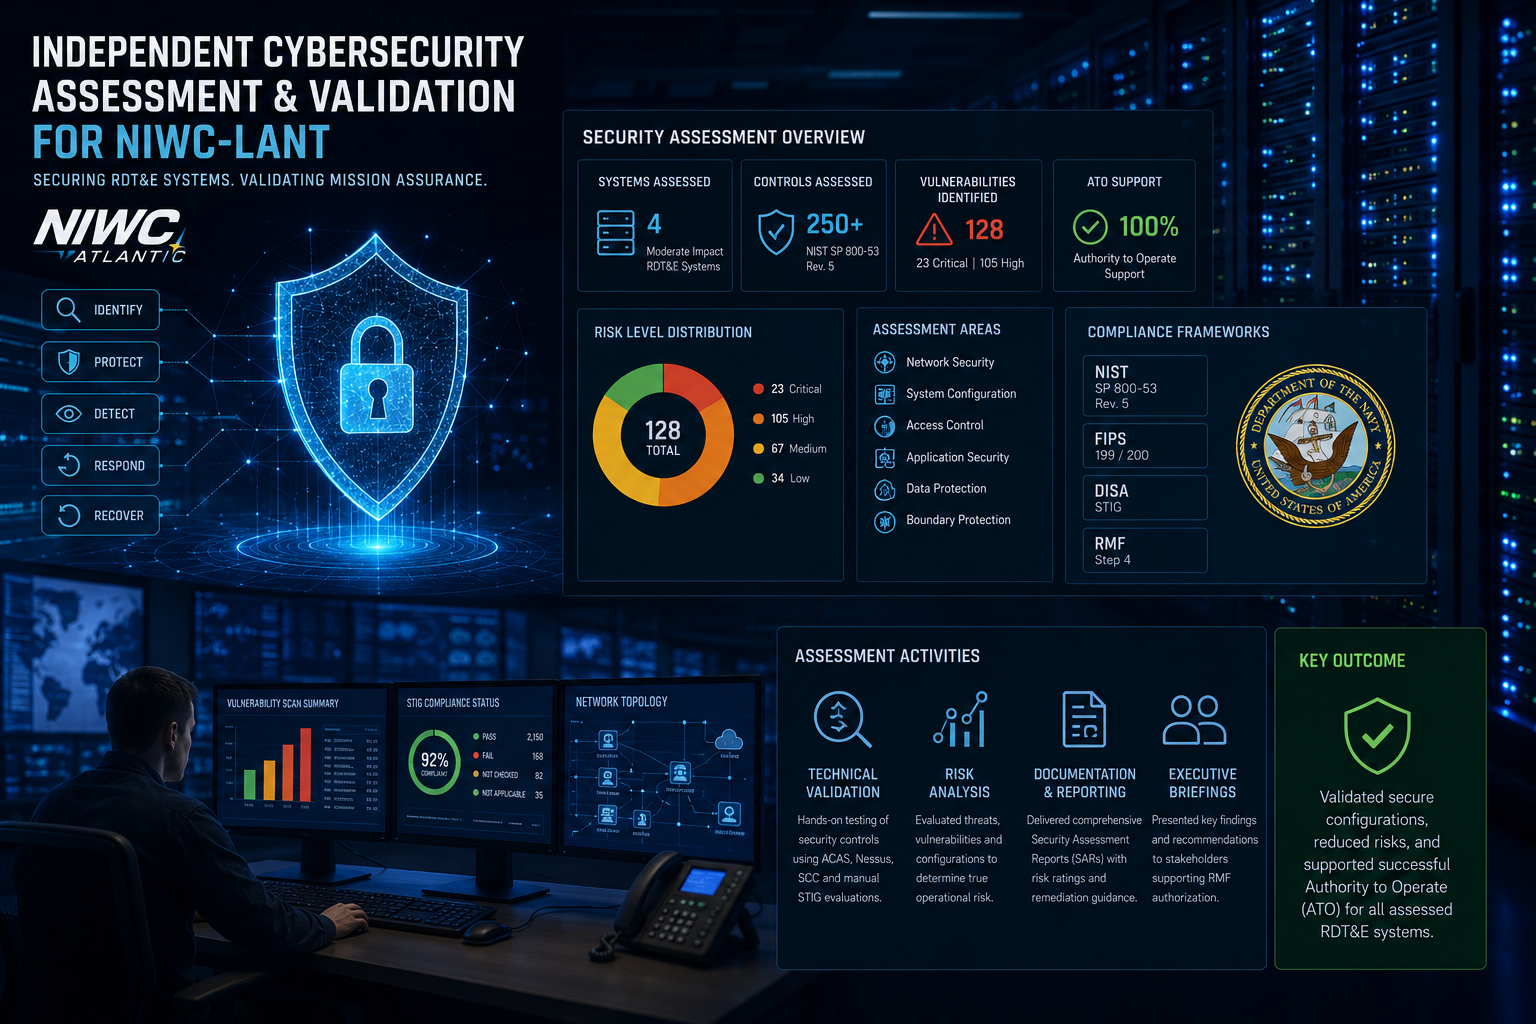
Independent Cybersecurity Assessment & Validation for NIWC-LANT
Served as a Navy Qualified Validator (NQV) conducting independent cybersecurity assessments for four Moderate-Impact Research, Development, Test, and Evaluation (RDT&E) systems. The project focused on validating NIST SP 800-53 security controls, performing technical security assessments, and supporting successful Authority to Operate (ATO) approvals.
- Security Control Assessment
- RMF Step 4 Validation
- FIPS 199 Categorization
- Independent Verification
- Nessus & ACAS Scanning
- DISA STIG Compliance
- Risk Assessment Reports
- Authority to Operate (ATO)
Performed independent security validation for multiple Navy RDT&E environments by reviewing authorization boundaries, assessing security controls, and validating compliance with federal cybersecurity standards. The project ensured secure deployment while supporting mission-critical research operations.
Strategy
Developed Security Assessment Plans, validated system categorization, and defined assessment methodologies to ensure complete RMF compliance across multiple enterprise environments.
Design
Performed technical control validation using vulnerability scanning, STIG compliance reviews, network segmentation analysis, and software security assessments to identify operational risks.
Features
- ecurity Assessment Plans
- Vulnerability Validation
- Network Segmentation Review
- Executive Risk Reporting
Conducted detailed vulnerability analysis across Windows Server, Red Hat Enterprise Linux, and Cisco environments. Assessment findings were documented with remediation guidance, helping stakeholders reduce security risks while maintaining operational effectiveness.
 Research
Design Process
Reviewed NIST security controls, DISA STIG requirements, FIPS 199 categorization, and system architectures to establish a comprehensive security assessment framework.
Executed vulnerability assessments, verified security implementations, analyzed compliance gaps, documented findings, and delivered comprehensive Security Assessment Reports supporting RMF authorization.
This project strengthened the cybersecurity posture of multiple Navy RDT&E systems by delivering independent security validation, reducing critical vulnerabilities, and supporting successful Authority to Operate (ATO) approvals while improving assessment efficiency.